Node-RED Authentication
The Servicely Node-RED Nodes currently support Basic and HMAC Header Token authentication. HMAC Header Token validation is the preferred method, as it provides authentication using a shared secret that is not transferred as part of the message exchange (as is the case with Basic and Bearer authentication).
This functionality requires version 0.0.17 of the node-red-contrib-servicely package
Creating servicely credentials
More detailed information on the configuration of the inbound Authentication Tokens can be found here: Inbound Authentication for Integrations.
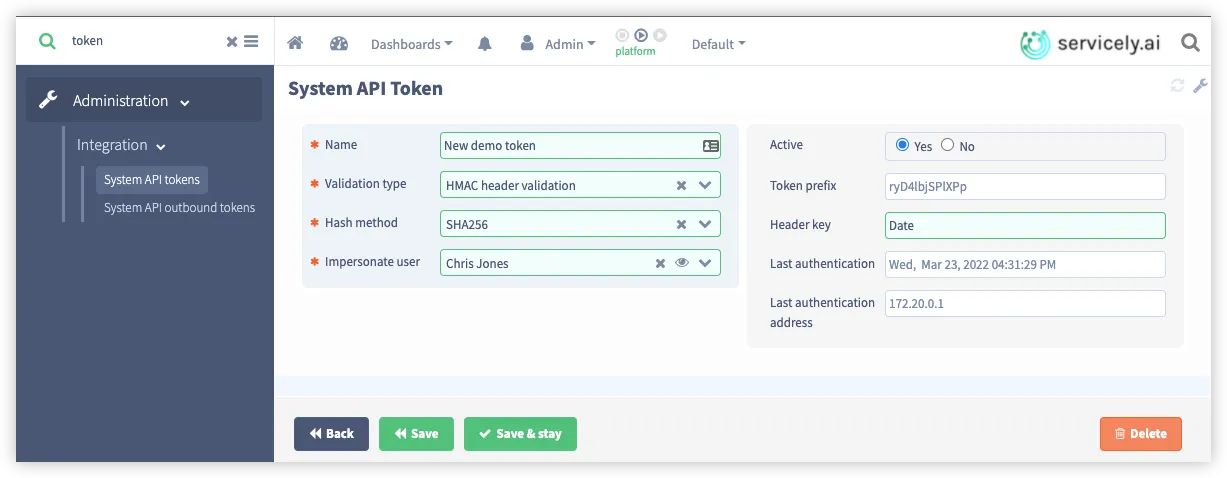
Version 0.0.17 of the Node-RED plugin requires a token with the following settings:
Field | Value |
|---|---|
Validation type | HMAC header validation |
Hash method | SHA256 |
Header Key | Date |
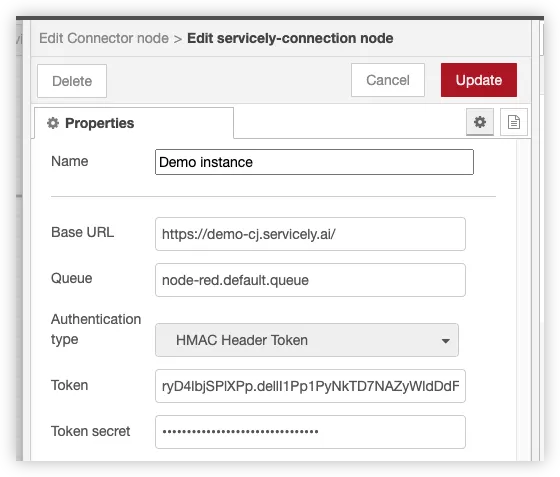
In a Node-RED Servicely Connection, specify the ‘HMAC Header Token’ Authentication type and paste the token and secret.